Monitoring is the system that keeps payment infrastructure aligned with changing network reality
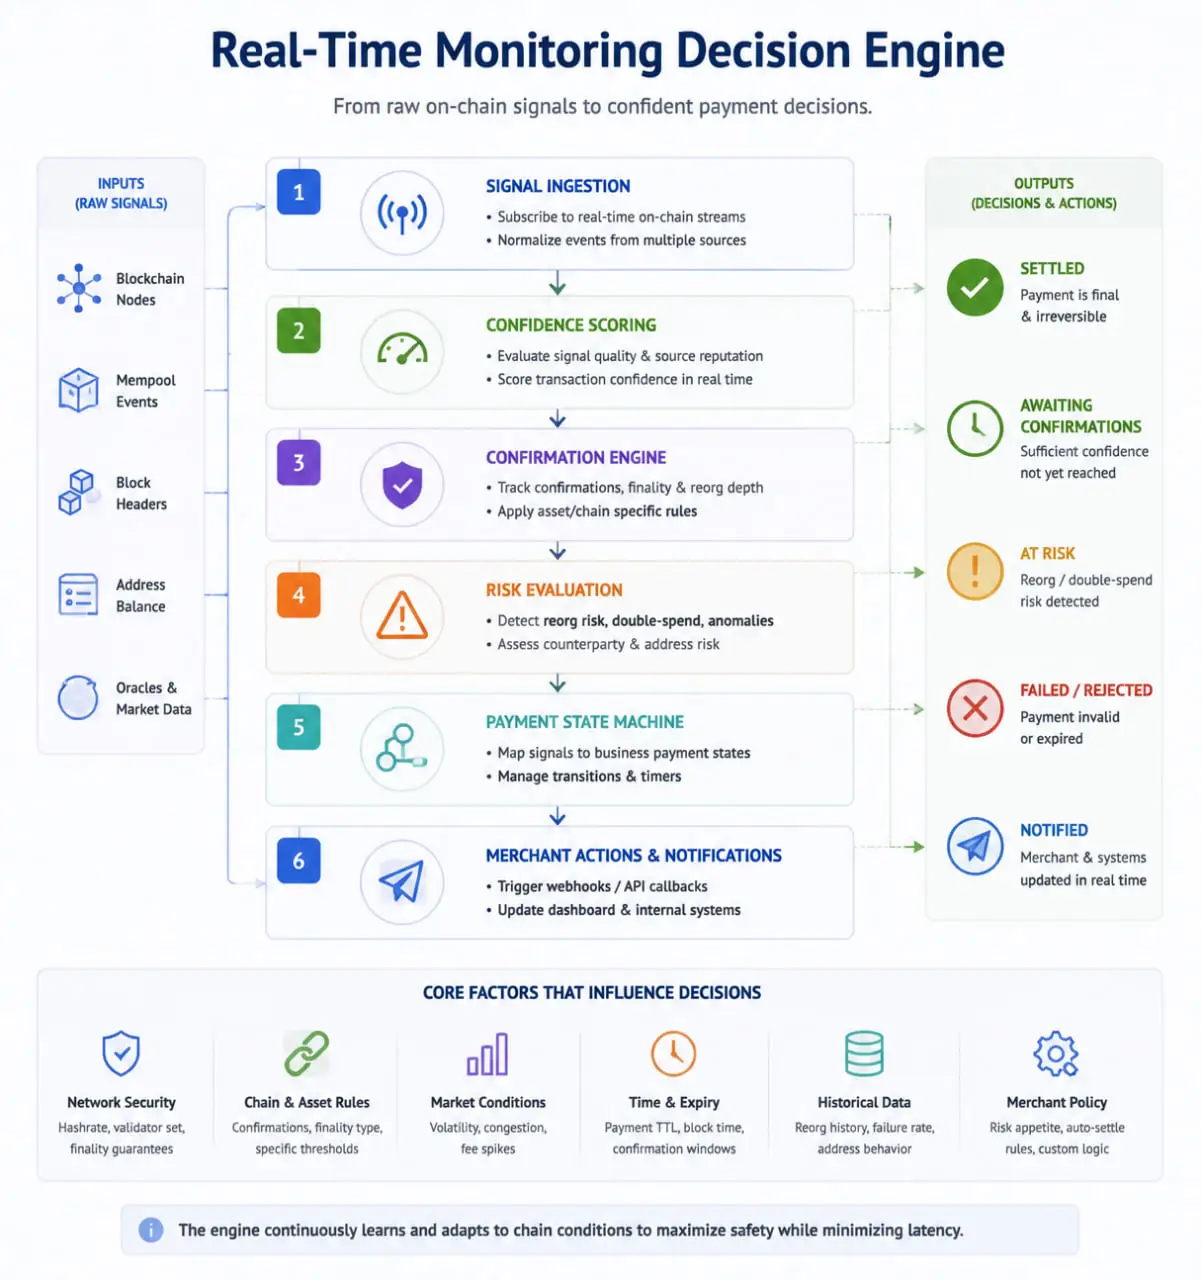
A blockchain payment system never receives one permanent answer from the network. It receives a sequence of observations. A transaction may first appear as pending, later enter a block, gain a stronger finality signal, or move backwards after a chain reorganization. A provider may also return stale data or miss an event entirely.
Real-time monitoring exists to follow those changes continuously. It observes network sources, compares their views, detects gaps, tracks canonical chain state, and publishes normalized evidence to the rest of the payment platform.
That evidence is not the final merchant decision. Monitoring answers questions such as: What did the network report? How fresh is the report? Do independent sources agree? Has the transaction changed position? Is the network or data source degraded?
Real time means continuously updating and correcting state—not promising instant certainty
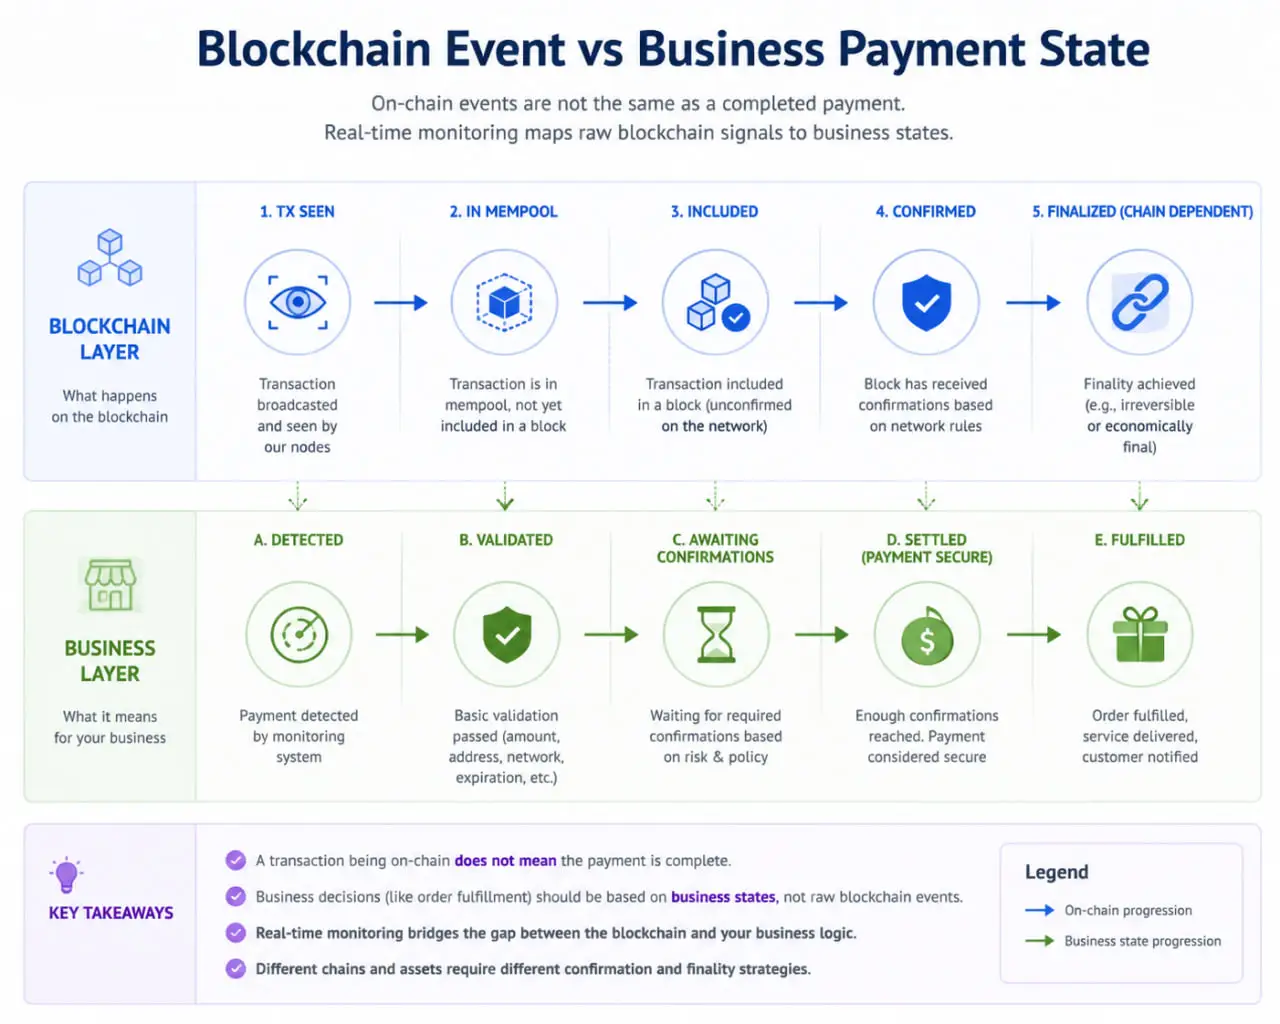
In payment infrastructure, “real time” is often misunderstood as “instant.” The more useful definition is continuous awareness with bounded delay. The system should discover relevant changes quickly, preserve their order, and correct its view when stronger evidence appears.
A fast notification can still be weak evidence. A mempool event may arrive in milliseconds, while block inclusion or protocol finality takes longer. Real-time monitoring should expose that progression instead of collapsing every stage into one paid or unpaid label.
- Detection latency How quickly did the system observe the event?
Low latency improves feedback, but does not increase the strength of the underlying network signal.
- Evidence freshness How current is the system’s view?
A response may be technically valid yet too old to support a payment decision.
- Correction ability Can earlier observations be revised safely?
Reorgs, dropped transactions, provider recovery, and late data all require corrective events.
- Traceability Can the system explain why its view changed?
Every important update should retain source, time, block identity, and processing context.
This distinction matters for customer experience. A checkout can acknowledge that a payment was detected without implying that fulfillment is approved. Clear intermediate states reduce confusion without weakening risk controls.
Production monitoring combines event streams, RPC queries, and historical backfill
No single access method is enough for a reliable payment platform. Push-based streams are fast, but a disconnected client may miss events. Polling is slower, but it can verify current state and recover gaps. Indexed historical data supports backfill and reconciliation after outages.
Bitcoin Core can publish transaction and block notifications through ZeroMQ while its RPC interface provides polled access to blockchain and mempool data. Geth exposes JSON-RPC subscriptions so applications can receive new heads and logs without polling every change.
- Push stream Receive blocks, transactions, logs, or slots with low delay
Best for fast awareness, but requires reconnect handling and gap detection.
- RPC verification Query authoritative fields when a decision needs confirmation
Useful for block identity, receipt status, transaction location, chain height, and source health.
- Historical backfill Recover events after downtime or subscription loss
Backfill should resume from a durable cursor, block, slot, sequence, or timestamp.
- Independent source Compare a second provider or node before trusting sensitive changes
Independence matters more than simply creating multiple connections to the same upstream.

Different nodes and providers can report different versions of the same moment
A node’s mempool is local. Its peers, relay policies, resource limits, and connectivity shape what it sees. RPC providers may also differ in indexing delay, pruning, supported methods, cache behavior, or commitment defaults. Two valid responses can therefore disagree temporarily.
This does not mean the platform should require a simple majority for every event. Three endpoints backed by one provider are not three independent observations. A stronger design scores sources by independence, freshness, historical reliability, chain position, and the type of evidence returned.
- Freshness Is the node close to the current chain head?
Track height or slot lag, last update time, and sync state before using the response.
- Independence Does this source provide a genuinely separate network view?
Different regions, operators, clients, and infrastructure paths reduce correlated failure.
- Agreement Do block hashes, transaction positions, and finality markers align?
Compare strong identifiers, not only human-readable status labels.
- Capability Can the source provide the detail this decision requires?
A fast balance endpoint may be unsuitable for log-level payment verification.
The safest response to severe disagreement is usually to reduce confidence, preserve the raw evidence, and delay irreversible actions. Guessing which source is correct may turn an upstream data problem into a financial loss.

Tracking a transaction requires tracking the chain around it
A transaction is not safely monitored by storing only its hash and confirmation count. The system should also retain the block or slot where it appeared and the canonical head used for that calculation. It should preserve the parent relationship and strongest finality marker.
Block height alone is not enough. Two competing blocks can exist at the same height. Monitoring should compare block hashes and ancestry so it can detect when a previously accepted branch is no longer canonical.
- First seen When and where was the transaction first observed?
Preserve source identity and whether the signal came from a mempool, block, log, or indexed stream.
- Inclusion identity Which block, slot, transaction index, or receipt contains it?
Strong location data allows the system to detect replacement or canonicality changes.
- Chain progression How has support for that inclusion changed?
Depth, safe or finalized tags, commitment levels, or other chain-native signals must update over time.
- Correction What happens if the transaction loses its previous position?
Emit an explicit corrective event and preserve both the old and new evidence.
Ethereum’s JSON-RPC supports the block tags safe and finalized, while Solana RPC methods and subscriptions use commitment levels such as processed, confirmed, and finalized. A monitoring engine should consume these chain-native signals instead of translating every network into a generic Bitcoin-style confirmation count.
Normalize event meaning without hiding chain-specific evidence
Multi-chain systems need a common event vocabulary. Without normalization, every downstream service must understand Bitcoin transactions, EVM logs, Solana instructions, TRON events, TON traces, and provider-specific responses.
But normalization becomes dangerous when it erases important differences. A field called finalized should not imply the same trust model on every network. The normalized event should retain the raw
chain status, source, block identity, and adapter version used to interpret it.
- Event identity A stable key for deduplication and replay
Include chain, event type, transaction identity, source position, and event version.
- Observed evidence The exact facts reported by the network source
Preserve block hash, slot, receipt, logs, output, amount, token contract, and raw status where relevant.
- Interpretation The adapter’s normalized meaning
Examples include transaction_detected, inclusion_changed, finality_updated, or source_degraded.
- Provenance How, when, and by which component was the evidence obtained?
Provenance makes disputes, incident review, and reprocessing explainable.
Each network needs a native observer behind the shared monitoring interface
A chain adapter should understand the network’s transaction model, streaming methods, finality signals, token representation, indexing gaps, and failure modes. The adapter then emits normalized events without pretending that all networks behave the same way.
- Bitcoin and UTXO chains Observe transactions, blocks, inputs, outputs, replacement signals, and chain tips
Bitcoin Core offers ZMQ notifications and an extensive RPC interface for mempool and blockchain queries.
- Ethereum-compatible chains Observe new heads, receipts, logs, token contracts, and finality tags
Subscriptions provide fast events; RPC verification confirms receipt status, block identity, and canonical position.
- Solana Observe signatures, accounts, logs, slots, blocks, and commitment levels
Solana’s official payment guidance recommends stronger indexing infrastructure for high-volume production monitoring.
- TRON Observe transactions and contract events through the network’s event services
TRON documents event plugins and built-in message queue options for real-time on-chain event consumption.
- TON Observe account transactions, traces, messages, and indexed streaming updates
TON’s streaming documentation warns that live streams do not recover past events, so backfill remains necessary.
Useful primary references include the Bitcoin Core RPC index and the Solana RPC overview. Solana also provides payment indexing guidance. TRON documents event subscription, while TON documents its Streaming API.

The monitoring system itself must be observable
Watching the blockchain is not enough. Teams must also know whether their listeners, queues, providers, adapters, and backfill workers are functioning correctly. A silent monitoring failure can be more dangerous than an obvious outage because the platform may continue presenting stale confidence.
OpenTelemetry describes observability through signals such as traces, metrics, and logs. Prometheus guidance emphasizes request count, errors, latency, in-progress work, queue depth, and heartbeat-style monitoring for multi-stage processing systems.
- Chain freshness Head lag, slot lag, finalized lag, and time since last block
These metrics show whether a source is current enough to support payment updates.
- Source quality RPC latency, error rate, disagreement rate, and reconnect count
Provider health should be measured separately by network, region, and operation.
- Pipeline health Event lag, queue depth, processing latency, and last successful cursor
A healthy node is not useful if events are stuck inside the platform.
- Data integrity Duplicate rate, gap count, correction rate, and backfill volume
Integrity metrics reveal when streaming and historical views do not align.
- Payment impact Payments waiting on evidence, age of oldest pending item, and delayed status updates
Technical monitoring should always connect back to merchant impact.
A useful service-level objective might limit the delay between a qualifying chain event and its normalized event. Another might require every subscription gap to be backfilled within a defined period. These objectives are more actionable than a dashboard that only shows node uptime.
Every real-time stream needs a recovery path for events it did not deliver
Connections fail. Processes restart. Providers rate-limit clients. A WebSocket can reconnect successfully while the application has already missed several blocks or events. The system must treat gap recovery as part of normal operation, not as a rare incident.
- Durable cursor Record the last fully processed block, slot, sequence, or provider cursor
The cursor should advance only after the event is safely stored.
- Overlap window Re-read a small range around the cursor after reconnecting
Overlap reduces edge-case loss and requires deterministic deduplication.
- Historical comparison Compare streamed events with canonical block or indexed history
Any difference becomes a backfill, correction, or investigation task.
- Degraded mode Reduce automated trust when observation quality falls below policy
The platform may continue collecting evidence while pausing irreversible completion decisions.
Event ingestion is usually designed for at-least-once delivery because replay is safer than silent loss. That choice requires stable event identities and idempotent consumers. Full business-effect idempotency belongs downstream, but monitoring must provide the identifiers and ordering context that make it possible.
Monitoring finds candidate activity; payment matching decides whether it belongs to an order
A listener may observe a transfer to a known address, token contract, memo, or destination tag. That is only a candidate payment event. Matching must still verify the expected network, asset, amount, payment reference, and validity window.
Keeping this boundary clear improves system quality. The monitoring layer should preserve every relevant fact. The matching layer should apply payment context and return an explicit result such as exact match, underpaid, overpaid, late, ambiguous, or unrelated.

State machines and webhooks consume monitoring evidence, but they solve different problems
The monitoring layer should not become the entire payment platform. A payment state machine decides how evidence changes business state. A webhook dispatcher delivers those changes to merchant systems. Reconciliation later verifies that blockchain, payment, and accounting records remain aligned.
These services need clear contracts. Monitoring should publish corrections when chain evidence changes. State transitions should reject invalid moves. Webhook delivery should tolerate retries. Merchant systems should query current payment information when a notification is missing or arrives out of order.


OxaPay exposes monitored payment progress through queryable states and signed callbacks
The internal architecture of a payment provider is not fully visible from public documentation. Merchants can evaluate the provider’s external contract. This includes payment identity, exposed states, status delivery, and the ability to query current information.
OxaPay’s Generate Invoice API supports a callbackUrl for payment updates and returns a unique track ID for the payment session. The payment status table distinguishes states such as new, waiting, paying, paid, underpaid, refunded, and expired.
OxaPay’s webhook documentation describes signed JSON callbacks, HMAC validation, status changes, and retry behavior. Merchants can also use the Payment Information API to retrieve current payment details rather than relying only on one notification.
- Stable payment identity Store the track ID and merchant order ID together
This creates a reliable bridge between the payment session and the business record.
- Signed status updates Validate the callback before changing internal state
Authenticity checks should happen before fulfillment, crediting, or accounting actions.
- Query fallback Use current payment information when delivery is delayed or uncertain
A queryable source helps recover after local outages or missed merchant-side processing.
- Platform health Check service availability during operational incidents
The documented System Status API can support integration health checks.
Merchants integrating directly can review the Merchant API documentation. The practical lesson is broader than one provider. Use callbacks for prompt updates and authenticated queries for recovery. Keep your own durable payment record for business continuity.
A production monitoring layer should pass these operational tests
- Source design Are critical networks observed through independent and measurable sources?
Count operational independence, not only endpoint quantity.
- Hybrid intake Does every push stream have RPC verification and historical backfill?
A stream without recovery eventually creates silent data loss.
- Canonical tracking Are block hashes, ancestry, transaction positions, and finality markers retained?
Confirmation counts alone are not enough for safe correction.
- Event contract Can every event be deduplicated, replayed, versioned, and traced to its source?
Recovery depends on stable identity and provenance.
- Chain fidelity Does each adapter preserve native status and trust assumptions?
Unified labels must not erase meaningful network differences.
- Self-observability Can operators detect stale sources, pipeline lag, gaps, and merchant impact?
The monitoring platform must reveal when it is no longer trustworthy.
- Degraded behavior Does the system reduce automated trust when evidence quality falls?
Failing visibly and conservatively is safer than silently presenting stale certainty.
- Separation of concerns Are monitoring, matching, state transitions, delivery, and reconciliation separate?
Clear boundaries reduce hidden policy and make each layer easier to test.
Official technical sources for further study
The following sources are maintained by protocol teams, core-client projects, or established observability standards. They are useful when implementing the concepts discussed in this article.
- Bitcoin Core ZeroMQ notification documentation
Official event-notification design and its relationship to polled RPC access.
- Ethereum and Geth Real-time JSON-RPC events
Official publish-subscribe interface for new heads, logs, and other events.
- Solana WebSocket RPC methods
Official subscriptions and commitment-aware event delivery.
- TRON Event Subscription framework
Official mechanisms for consuming real-time on-chain events.
- TON Payment processing overview
Official guidance on off-chain monitoring for real business payment flows.
- Observability standards Prometheus instrumentation practices
Metrics guidance for online services, queues, batch stages, failures, latency, and heartbeats.